
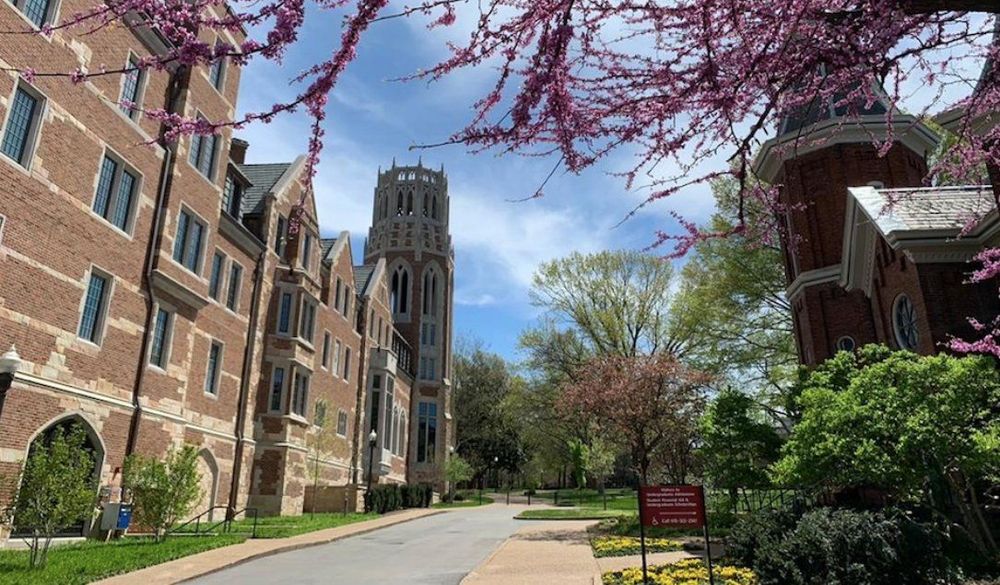
Vanderbilt cybersecurity incident impacting campus devices and systems
Vanderbilt University announced a cyberattack on Monday morning, warning students and employees that campus devices and systems may be impacted by the incident.
A spokesperson for the Nashville-based university told Recorded Future News their IT team is “actively investigating and working to contain the situation.”
Vanderbilt University posted a longer statement on social media asking everyone to shut down their devices, disconnect from university WiFi, and “remain extremely vigilant.”
They warned that anyone who notices suspicious activity on their devices — like pop-ups, security warnings, changes to files and password requests — should turn the device off and report it to campus IT officials.
Vanderbilt University, one of the premiere higher education institutions in the country, serves about 14,000 students and has more than 6,000 staff members.
Vanderbilt University Medical Center was previously attacked by a ransomware gang in 2023.
The attack emerged early Monday after the ransomware gang BYOD added the university to its leak site and made several claims about stolen data.
The group has staged several high-profile attacks in recent weeks, including an incident involving Michigan State University and the University of New Mexico.
The attack on the University of New Mexico caused alarm because it also impacted the school’s medical facilities, forcing one of the state’s only top-tier hospitals to turn away ambulances.
Ransomware expert Allan Liska said BYOD has been ramping up as of late but only emerged recently.
“We didn’t see their first victim until Sept 29th,” he said.
The group is believed to have carried out an attack on Trump Mobile and to have subsequently leaked data from 3,615 prominent customers, which drew Congressional scrutiny.
Multiple cybersecurity firms released reports last week warning of startling increases in ransomware attacks this year as artificial intelligence tools proliferate across the cybercriminal ecosystem.
Halcyon said it saw a 40% increase in ransomware activity between July and September – with 111 groups claiming 2,766 attacks against organizations in 122 countries.
Trellix added that the number of ransomware groups and victim posts reached record numbers from April to September, with new groups accounting for a third of all posts in August.
“The fragmentation is structural: power is distributed across a wider field of operators, each moving faster and requiring less infrastructure than before,” Trellix researchers said.

Jonathan Greig
is a Breaking News Reporter at Recorded Future News. Jonathan has worked across the globe as a journalist since 2014. Before moving back to New York City, he worked for news outlets in South Africa, Jordan and Cambodia. He previously covered cybersecurity at ZDNet and TechRepublic.