
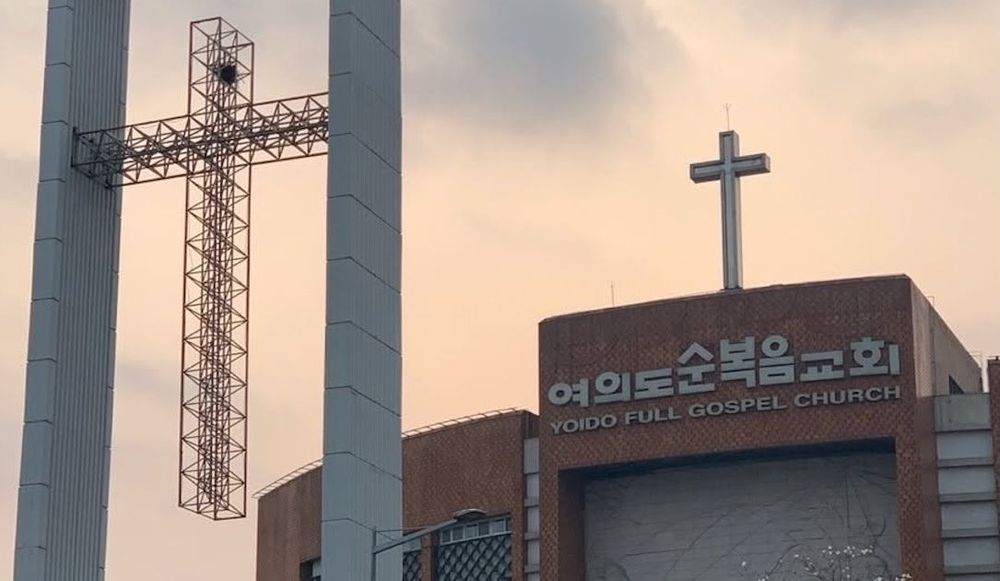
Hackers target two South Korean megachurches, potentially exposing congregant data
Two of South Korea's largest Protestant churches are investigating cyberattacks that may have exposed sensitive information about hundreds of thousands of members, including personal details, financial records and internal documents.
Seoul-based Yoido Full Gospel Church and SaRang Church acknowledged the suspected breaches after South Korean cybersecurity firm Oasis Security published research this week analyzing data recovered from a server used by the attackers.
In a statement to local media on Wednesday, Yoido Full Gospel Church said it had identified one dataset containing personal information associated with approximately 850,000 members.
The church previously said it had been notified by South Korea's internet security agency about a suspected breach of personal information involving its systems. It is working with authorities and cybersecurity specialists to determine the extent of the incident and prevent further damage.
SaRang Church also confirmed to local media that it was investigating a suspected cyberattack and taking steps to prevent additional damage. It has not disclosed how many people may have been affected or identified the attackers.
The incidents came to light after Oasis Security researchers analyzed files recovered from an attacker-controlled server located overseas. The researchers did not publicly identify the two churches in their report but described separate intrusions involving large South Korean religious organizations.
In one case, researchers recovered more than 47 gigabytes of data, including personal information, financial records, internal communications and administrative documents.
The attackers installed a web shell — malicious software that allows hackers to remotely control a compromised server — and used it to gain administrator-level access to the organization's internal systems.
From there, they accessed databases and other parts of the network, collecting church membership information, payroll and accounting records, internal messages and employee login credentials.
Researchers also found evidence that the attackers accessed a network storage system containing internal reports and backups.
The second intrusion involved a different method. Hackers used previously leaked passwords and security flaws in internal applications to access accounts and information they were not authorized to view. Some of the vulnerabilities also allowed them to reset other users' passwords.
The attackers subsequently accessed the organization's SAP software, used to manage business operations and employee information.
According to Oasis Security, the compromised records included personal information associated with approximately 89,000 church members and human resources files for 286 employees, including the senior pastor. The attackers also accessed information connected to a college ministry, including records relating to students and staff.
The researchers said the intrusions likely occurred in August, weeks before the incidents became public.
Their investigation also found that the attackers reused infrastructure associated with an earlier compromise of an unnamed U.S.-based Christian content platform, suggesting a technical connection between the incidents.
The researchers did not identify the hackers, establish their nationality or determine why the religious organizations were targeted.
Oasis Security also reported evidence that the attackers used artificial intelligence, including for analyzing vulnerabilities, examining software, moving through internal networks and extracting data.
Both churches are among South Korea's most prominent Protestant congregations. Yoido Full Gospel Church has historically reported a membership of around 800,000, making it one of the world's largest Protestant churches. SaRang Church operates a large worship complex in Seoul and runs numerous ministries serving children, students and young adults.

Daryna Antoniuk
is a reporter for Recorded Future News based in Ukraine. She writes about cybersecurity startups, cyberattacks in Eastern Europe and the state of the cyberwar between Ukraine and Russia. She previously was a tech reporter for Forbes Ukraine. Her work has also been published at Sifted, The Kyiv Independent and The Kyiv Post.