
EU cyber law won’t force fixes for fridge controllers hit in French attack
The European Union’s new cyber rules require manufacturers to report attacks exploiting their end-of-life products, but does not force them to fix the issues, the bloc’s cybersecurity agency said Monday, after a cyberattack hit hundreds of French supermarkets’ refrigeration systems.
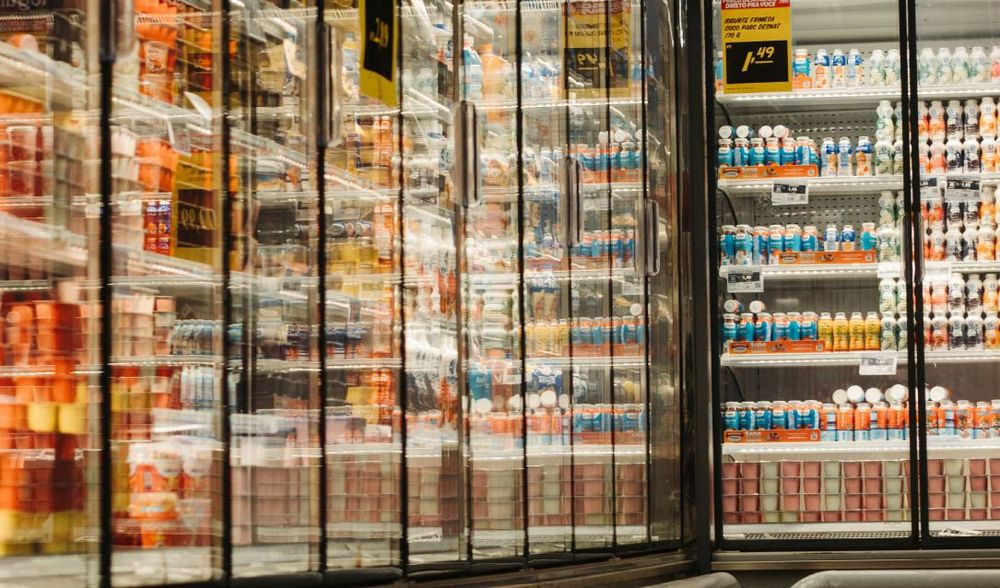
Earlier this month, hackers compromised internet-exposed remote controllers for refrigeration systems at numerous French supermarkets, forcing some units into a continuous defrost cycle at 50°C, according to reports at the time.
Grocery chains including Intermarché, Carrefour, Monoprix, Leclerc and Coopérative U were affected, with monetary losses estimated in the tens of millions of euros as spoiled food stock had to be thrown away.
France’s cybersecurity agency ANSSI said it was “aware of the compromise of refrigeration system remote controllers,” naming Danfoss’s AK-SM and AK-SC series, Copeland’s xweb and Dixell’s xweb products.
The agency’s emergency response team, CERT-FR, issued an alert last Monday and ANSSI urged operators to disconnect or filter any controllers exposed to the internet to prevent further attacks.
“Investigations are on-going,” the agency told Recorded Future News, adding that it was coordinating preventive and remediation measures across sectors that might be affected, “with a specific focus on mass retailers.”
In a statement, Copeland acknowledged “the vulnerability identified in a discontinued, end-of-life generation of controllers,” adding it was “currently working with impacted customers to mitigate the risk.”
The company said it would “continue to support customers in strengthening cybersecurity through supported products, current software and industry-recommended practices.” It did not say how many customers were affected.
Danfoss did not respond to a request for comment, but has said its affected units were also end-of-life.
The Paris prosecutor’s office told Recorded Future News it had received “about ten complaints” and estimated the “number of victims at around 700.” Its investigation is also ongoing, and it said that to date no perpetrator has claimed responsibility for the attack.
EU response
Provisions of the EU’s Cyber Resilience Act that took effect last month require manufacturers of connected hardware and software devices sold in the bloc — from consumer gadgets to industrial controllers like those hit in France — to report actively exploited vulnerabilities and severe incidents affecting their products.
ENISA — the European Union Agency for Cybersecurity — told Recorded Future News that the obligation covers end-of-life products “no longer sold in the EU, but which remain in use,” and that “the reporting obligations continue to apply after a product with digital elements is no longer supported.”
However the law’s separate obligations to handle vulnerabilities, including fixing them and issuing free security updates, apply only during a product’s support period, which manufacturers define.
Where a product was placed on the market before December 11, 2027, or its support has ended — as in the fridge controllers targeted in this instance — “the manufacturer is not required to comply with the vulnerability handling obligations,” said ENISA.
The agency declined to share information on specific notices it may have received from manufacturers and would not say whether any had reported the attacks. It said the EU CSIRTs Network of national cyber emergency response teams “is actively exchanging info and monitoring the situation.”
ANSSI added it was also “equally mobilized at the European level and is maintaining regular dialogue with its counterparts.”
No longer supported
The Danfoss equipment named in the attack had been retired for years. Some was phased out in 2016, with a final purchase deadline that October, while other product lines were declared end-of-life in 2021. As such, neither receives software or security updates.
In an October newsletter last year, Danfoss said it was enforcing a “hard End of Service” policy for those and other legacy products, citing “recent European cybersecurity legislation.” Continuing support, it said, “would place Danfoss under new legal obligations to maintain security updates.”
The newsletter referenced earlier attacks involving its controllers, including a campaign at the start of the Russian invasion of Ukraine in which attackers targeted Russian supermarkets using the controller. Another 40 stores were hacked in Israel, all of which Danfoss said lacked adequate firewall or VPN protection.
Aging equipment poses a persistent challenge for industrial and building control systems. Replacement can be costly and disruptive, leaving operators reliant on other safeguards. Guidance typically recommends isolating such systems on segmented networks and limiting internet access.
The EU’s Cyber Resilience Act will impose stricter requirements on future products from December 2027, when manufacturers must specify a support period that should reflect a product’s expected lifetime, potentially much longer for industrial equipment.
Separately, the EU’s revised Product Liability Directive, effective for new products this December, will allow products to be deemed defective if manufacturers fail to provide security updates within their control.
Neither measure applies retroactively, leaving existing equipment, including the controllers attacked in France, outside both regimes.

Alexander Martin
is the UK Editor for Recorded Future News. He was previously a technology reporter for Sky News and a fellow at the European Cyber Conflict Research Initiative, now Virtual Routes. He can be reached securely using Signal on: AlexanderMartin.79