
Harden cooling systems now, feds warn critical infrastructure operators amid attacks
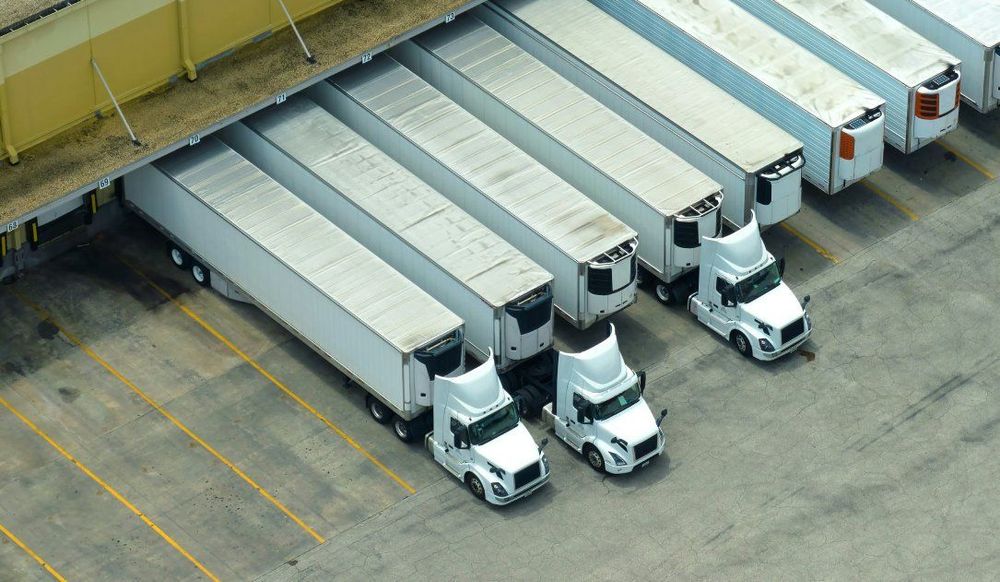
The U.S. government on Thursday called on critical infrastructure operators to safeguard their cooling systems following hacks that have caused chaos in European supermarkets in recent weeks.
The warning, issued by the Cybersecurity and Infrastructure Security Agency, the FBI and others, comes after hundreds of supermarkets across Europe had their refrigerators remotely hacked and temperatures raised, resulting in potentially millions of euros of spoiled food.
Earlier this week, cooling unit controls were tampered with at three of France’s national blood banks, the French Blood Establishment announced, though it’s unclear if the incidents are linked.
In their advisory, federal agencies noted that organizations in the healthcare, transportation, food and chemicals sectors “widely” use cooling systems that rely on “automated and remote monitoring of temperatures, continuous temperature logging, defrost cycle management, and energy optimization.”
They cautioned that malicious actors may exploit vulnerabilities in “unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating and defrost cycles, which can cause widespread inventory loss and equipment hazards.”
Federal officials asked critical infrastructure owners to boost their defenses by “using strong authentication, keeping systems updated, identifying any systems that are accessible from the internet, removing unnecessary remote access, and securing any necessary remote access.”
In August, freezers and refrigeration units at several U.S. military commissaries unexpectedly switched into defrost or heating modes, though it is unclear if those malfunctions are in any way connected to the recent wave of attacks. The Defense Department’s inspector general, among others, is investigating the various incidents.
No one has claimed responsibility for the recent cyberattacks in Europe, though authorities are on high-alert about potential hybrid threats to infrastructure amid tensions with Russia following Moscow’s invasion of Ukraine.
The Kremlin has repeatedly denied involvement in any hybrid warfare or sabotage operations.
Last year, a Dutch conglomerate responsible for several big-name American supermarket brands revealed that hackers had pilfered the personal information of more than 2 million people. The company, Ahold Delhaize, suffered another cyberattack in October that impacted online services across its European and U.S. brands.
Martin Matishak
is the senior cybersecurity reporter for The Record. Prior to joining Recorded Future News in 2021, he spent more than five years at Politico, where he covered digital and national security developments across Capitol Hill, the Pentagon and the U.S. intelligence community. He previously was a reporter at The Hill, National Journal Group and Inside Washington Publishers.