
Cyber experts call on CISA to create mandatory federal OT rules
A group of experts called on the nation’s federal cybersecurity agency to pass rules setting baseline cybersecurity standards for operational technology (OT) owned by federal agencies.
The Operational Technology Cybersecurity Coalition (OTCC) released a white paper on Tuesday urging the Cybersecurity and Infrastructure Security Agency (CISA) to create a new directive centered around operational technology, which is used to monitor and control critical infrastructure.
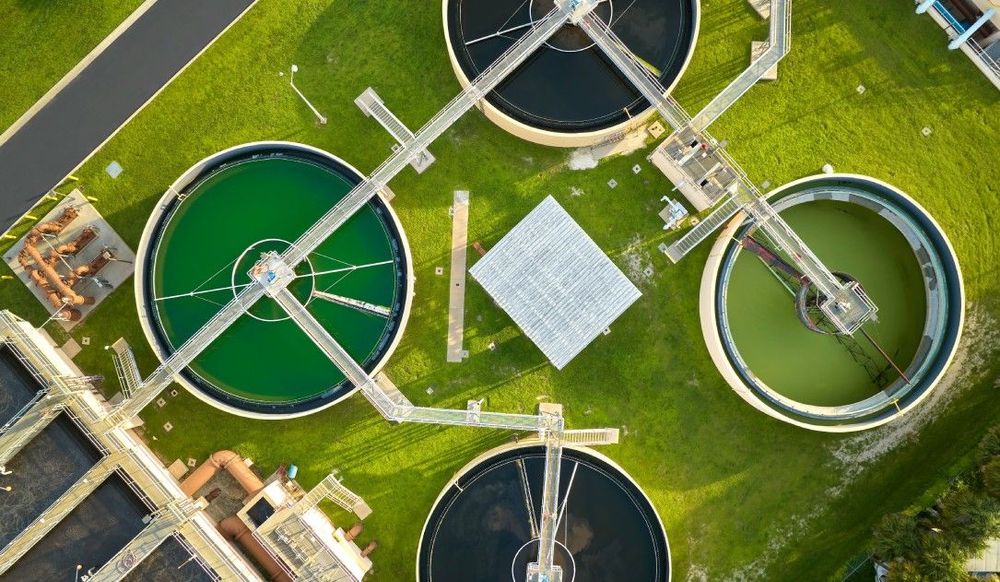
OTCC said the recent cyberattacks on hundreds of water systems in at least 12 U.S. states was a clear warning sign that operational technology has become a ripe target for both nation states and cybercriminals.
Much of the technology within the water systems that was impacted were devices that should not have been connected to the internet, had default passwords or no passwords at all and were not segmented from other non-operational parts of the network.
Federal civilian agencies rely on more than 8,000 owned or leased buildings that include laboratories, hospitals, research facilities, ports of entry and more — all of which have an array of HVAC, power, access control, water and building automation systems.
OTCC cited a recent study from a government watchdog that found only 7 of the 22 civilian agencies it reviewed had fully met White House requirements to inventory their networked operational technology and Internet of Things devices. The inventories were due in September 2024.
"[The Government Accountability Office] just confirmed what OT practitioners have been warning about for years: you can't secure what you can't see, and most federal agencies still can't see their OT," said Tatyana Bolton, executive director of OTCC. "Guidance alone hasn't closed that gap. A binding operational directive would give every agency a clear, enforceable baseline and give CISA the visibility to make sure it actually gets done."
Most federal civilian agencies govern OT systems on their own, leaving CISA blind to their security posture. Artificial intelligence has rapidly lowered the barrier for sophisticated attacks, making OT systems targets in a way they previously were not.
CISA has issued multiple binding operational directives that came after voluntary measures were not effective.
A directive would allow CISA to “drive consistent implementation and measure compliance across the government,” according to the OTCC paper.
“The value of a BOD is to establish a uniform, government-wide baseline so that CISA can understand, measure, and manage cyber risk consistently across the FCEB. While private or local entities are not required to implement BODs, they still provide a strong demand signal of what the government views as a cybersecurity best practice,” the experts said.
CISA declined to comment on the paper. Michael Garcia, policy director of OTCC, told Recorded Future News that they did engage with CISA while creating the paper and shared a final copy of the report before it was published.
The ‘gray zone’
The 8-page report lays out a prevention and containment baseline built on visibility into OT assets, network segmentation, enforceable remote access controls, configuration baselines, incident preparedness and verified backup and recovery.
The OTCC said CISA should require agencies to designate a senior official or unified office to manage OT asset inventory, configure baselines and prepare for potential incidents. Backup and recovery plans should be created alongside risk reports.
"Operational technology too often falls into a gray zone between the [Chief Information Officer’s] office and facilities management, and when no one owns it, no one secures it," Garcia said.
"Our recommendations are practical by design. Name an accountable official, build on requirements agencies already have, and prioritize the basics that matter most in the incidents we've seen, like changing default passwords and segmenting networks."
Several OT cybersecurity experts said ownership was the key aspect of the paper.
“In most facilities, the chillers, badge readers, and power systems belong to a facilities team, and the network belongs to the CIO. Every other recommendation on the list, from asset inventory to segmentation to remote access, assumes someone is accountable to act on it,” said Dave Williams, OT security leader at cybersecurity firm Elisity.
“Clear ownership for addressing cybersecurity risks settles in advance how priorities and resource constraints are resolved. A directive can force an agency to put a name on that responsibility, and that alone would do more than another round of guidance."

Jonathan Greig
is a Breaking News Reporter at Recorded Future News. Jonathan has worked across the globe as a journalist since 2014. Before moving back to New York City, he worked for news outlets in South Africa, Jordan and Cambodia. He previously covered cybersecurity at ZDNet and TechRepublic.