
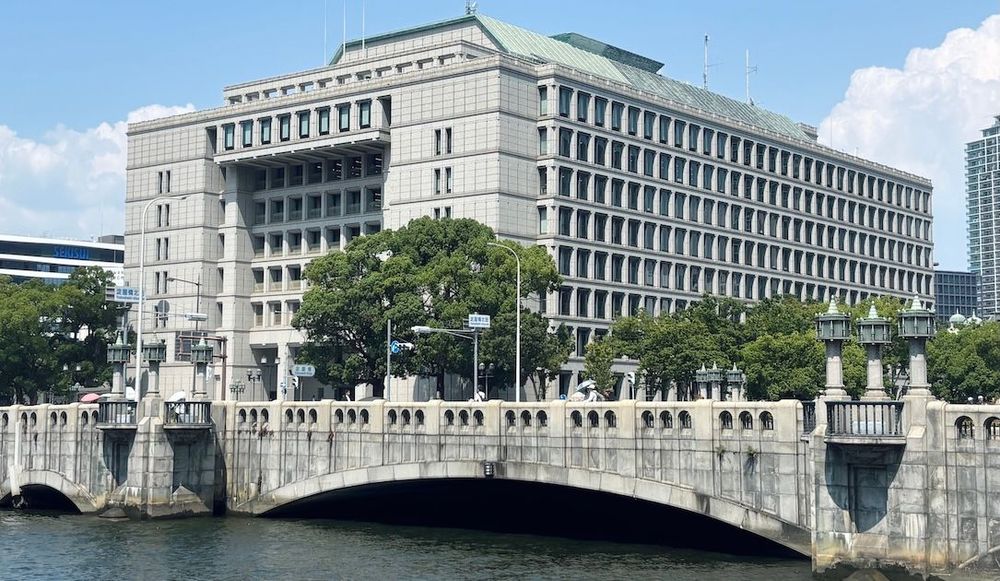
City of Osaka warns of data breach impacting 1 million as Japan reels from dozens of cyber incidents
The city of Osaka notified the public that a data breach involving a third-party technology provider exposed more than 1 million email addresses tied to an online administrative services platform.
According to a statement published by the government of Japan’s third-largest city, hackers accessed the Arara email distribution service used by TKC Corporation, the company contracted to maintain the administrative services platform.
Anyone who received an email from the system run by the city between July 2026 and October 31 had their email address leaked, according to the city. They warned the city’s 2.8 million residents to be wary of suspicious emails purporting to come from the city — urging everyone not to open any URLs or attachments.
The city breach came days after the regional government of the Osaka Prefecture announced its own data breach involving the information of food support program participants.
The attack on Arara has had a cascading effect on dozens of large businesses and governments in Japan. The company said a November 2 cyberattack exposed 77 million email addresses from nearly 400 customers, including TKC, gaming giant Sega and others.
Arara noted that hackers used their email distribution service to send millions of malicious emails pretending to be credit card companies and financial institutions.
‘Let us mobilize’
Japan has been rocked by months of cyberattacks on critical companies and institutions — from Japan Airlines to Sony Network Communications and gaming company Capcom.
Last week, Japanese Prime Minister Sanae Takaichi held a cabinet meeting on cybersecurity and announced a package of emergency measures aimed at increasing the use of AI for cyber defense, more robust information gathering, offensive cyberattacks and increased support for data breach victims.
About $62 million in emergency funds were dedicated to the effort and companies were urged to report cyberattacks more quickly to government agencies.
“Even at this very moment, incidents of unauthorized access and information leaks continue to occur, significantly affecting people's daily lives and business activities,” she said. “Let us mobilize the full resources of the government to strengthen Japan's overall capabilities to respond to cyberattacks.”
Japan's national Computer Security Incident Response Team published a study three weeks ago that said it found evidence attackers are using AI to scan for known vulnerabilities before carrying out attacks in the country.
Mihoko Matsubara, the chief cybersecurity strategist at Japanese telecom giant NTT, told Recorded Future News that recent data showed cyberattacks on Japanese systems began to grow in July and skyrocketed through October.
October saw 58% of all reported incidents this year in Japan, she said. About 380 million pieces of personal data have been stolen so far this year.
A large amount of Japanese personal information is already being traded on the dark web, and some of the data has been used for fraudulent securities transactions, Matsubara said, warning that determined actors with financial resources could compile a comprehensive database of Japanese citizens' socioeconomic activities and personal preferences.
Matsubara, who previously worked for Japan’s Ministry of Defense and other government cybersecurity committees, noted that the recent surge in breaches came after new cybersecurity legislation came into effect that allows the government to take more robust action in the event of a significant cyberattack.
“Many countries would be keen to learn how quickly Japan would respond to which kinds of cyberattacks, and with what level of intensity,” she said.
Matsubara added that the recent breaches appear to involve AI-tools like Claude and Artex, which help cybercriminals uncover and exploit bugs. But she argued that not every breach in this wave can be attributed to AI.
The most important aspect of the government initiatives announced last week is the acknowledgement that cybersecurity “cannot be left entirely to individual organizations.”
“Government assistance, in the form of security assessments and incident response or recovery support, can make a difference when push comes to shove,” she said. “However, the funding needs to be the beginning of a consistent longer-term effort, and cannot be seen as a one-time quick fix to the current wave of attacks.”

Jonathan Greig
is a Breaking News Reporter at Recorded Future News. Jonathan has worked across the globe as a journalist since 2014. Before moving back to New York City, he worked for news outlets in South Africa, Jordan and Cambodia. He previously covered cybersecurity at ZDNet and TechRepublic.